
“Zero Trust” has become one of the hottest buzzwords in cybersecurity – but behind the hype, it represents a fundamental shift in how we secure systems and data. For years, companies relied on a “trusted network” model: anyone inside the corporate network was automatically trusted, while outsiders were kept out. Zero Trust flips that model on its head. The core idea of Zero Trust is simple: trust nothing and verify everything. Every user, device, and connection must continually prove it’s authorized – no exceptions, even for those already inside the network. This approach emerged because the old perimeter-based defenses (think firewalls and VPNs) aren’t enough in today’s world of cloud services, remote work, and sophisticated threats. Attackers have found ways to slip past perimeter defenses or exploit trusted insiders, so assuming breach and limiting trust is the new mantra. However, Zero Trust is often misunderstood as just a product or a marketing term. In reality, **Zero Trust is not a single product you can buy – it’s an architectural philosophy and strategy. It requires a combination of technologies and policies working together. Let’s break down what Zero Trust really means, and how it can significantly strengthen your organization’s security.
What Does “Zero Trust” Mean, Exactly?
At its heart, Zero Trust is about removing implicit trust from your systems. In a traditional network, for example, if Bob from accounting is on the office network, we might trust that Bob is who he says and allow him to reach internal finance servers without much scrutiny. Zero Trust
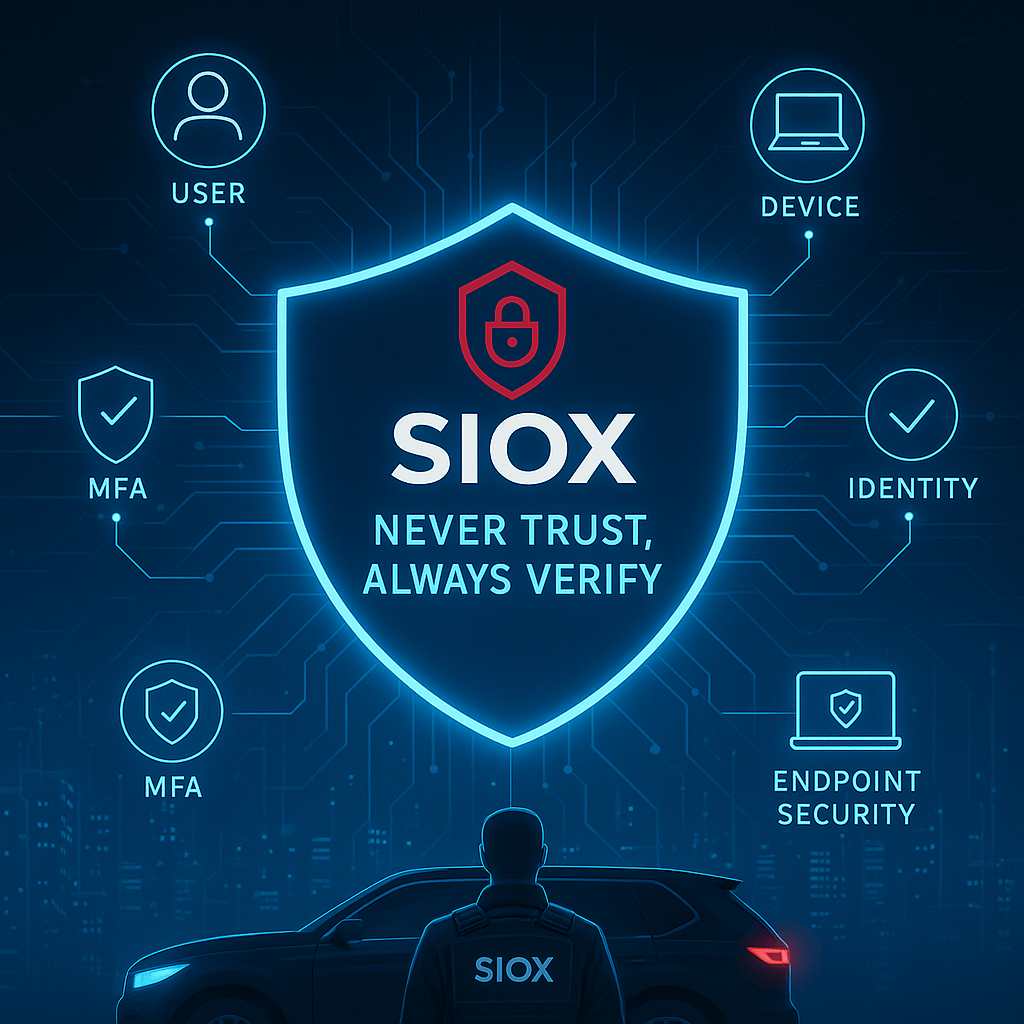
says: prove it. Just because Bob is on our network (or using a company laptop) doesn’t mean that device hasn’t been compromised or that it’s actually Bob and not a hacker using Bob’s credentials. So under Zero Trust principles, Bob would have to continuously authenticate (prove his identity), and his device’s security posture would be checked (is his laptop up to date on patches? running approved software?). Furthermore, Bob’s access would be limited to only what he truly needs – he wouldn’t automatically get to traverse the entire “trusted” network. In summary, Zero Trust means every access request is treated as untrusted by default, regardless of whether it originates from inside or outside the network. Only after verification of identity, context, and device health is access granted – and even then, only minimally. This “never trust, always verify” mindset underpins all Zero Trust decisions. It’s a significant change from the old approach, but it dramatically reduces the chances of an attacker who breaches one device or account from moving laterally through your systems.
Key Principles of Zero Trust Security
Adopting Zero Trust involves implementing several key principles across your technology and policies:
- Verify Identity Rigorously: Strengthen how users prove who they are. This means widespread use of multi-factor authentication (MFA), not just for VPNs but for every critical application and system. It also means integrating identity systems so that you have a single source of truth (like a secure identity provider) to authenticate everyone. Zero Trust calls for verifying the user’s identity continuously, not just at login – if something seems off (like an unusual location or time), the system might re-prompt for MFA or block access.
- Validate Device Posture: In Zero Trust, the device being used is just as important as the user. Every device – laptop, mobile, server – should be assessed for trustworthiness before it accesses resources. Is the device managed by the company? Is it running approved security software? Is it free of known compromises? Solutions like endpoint management and threat detection tools come into play here. For example, if an employee’s personal tablet isn’t up to security standards, Zero Trust rules might prevent it from accessing sensitive data. Only devices that meet your security requirements (patched OS, encryption enabled, etc.) get full access, and even then, they should re-verify regularly.
- Least Privilege & Micro-Segmentation: This principle means giving each user and system the minimum access required – nothing more. Rather than flat, open network access, you segment networks and cloud environments into smaller zones. An employee in HR, for instance, shouldn’t even “see” the servers used by engineering. If that HR account is compromised, the attacker hits walls at every turn because each segment requires separate authorization. Techniques like micro-segmentation break up your network so that even if a hacker gets in, they can’t freely roam everywhere at once. Likewise, user accounts are set up with limited privileges; admin rights are only granted when absolutely necessary (just-in-time access).
- Continuous Monitoring and Analytics: Zero Trust assumes that breaches will happen, so it emphasizes quick detection. Implement centralized logging and monitoring to get a real-time view of who is accessing what. Use behavior analytics to learn normal patterns, so you can spot anomalies (e.g., an account accessing data it never has before, or large data downloads at 2 AM). Modern security tools with AI can alert or automatically block these unusual activities. The idea is to catch potential intrusions early, since no single login or device is implicitly trusted. In a Zero Trust model, you’re always watching and ready to respond. As one expert put it, don’t just log an unusual 3 AM login from overseas – stop it and investigate immediately.
Why Zero Trust Matters
Moving to Zero Trust is a significant effort, but it directly addresses many of the failings of traditional security models. Consider how many recent breaches started with a single stolen password or a single infected machine – in a flat network, that often means the attackers could then escalate privileges and move laterally until they found crown jewel data. Zero Trust blocks that common attack path by compartmentalizing everything and enforcing checks at every step. It’s particularly relevant now because companies have data spread across on-premise servers, multiple cloud providers, and employees working from anywhere. The old idea of a “network perimeter” is blurry – there is no single wall to defend anymore. Zero Trust provides a framework to secure this new reality by essentially saying the perimeter is around every user and every device.
It’s important to note that adopting Zero Trust doesn’t happen overnight. It’s a journey of incrementally improving identity management, device controls, network design, and monitoring capabilities. Some organizations start with a pilot in one area (for example, implementing strict access controls for a sensitive database) and then expand the Zero Trust principles gradually. Leadership buy-in and user education are also critical, because Zero Trust may introduce more friction (like more frequent MFA prompts or access denials) – but that friction is there for very good reason. With executive support and clear communication, employees come to understand that these new measures are what keep the company safe from modern threats.
Far from being just a buzzword, Zero Trust is increasingly seen as a cybersecurity must-have for organizations of all sizes. When implemented correctly, it significantly reduces the likelihood of a catastrophic breach. As one security leader described, Zero Trust “is a response to the realities of modern cyber risk… when done right, it can transform your organization’s security posture”. Businesses that embrace Zero Trust find that they become more resilient, more agile, and far better prepared to fend off attacks. In an age where cyber threats are relentless and perimeter defenses are no longer enough, Zero Trust offers a robust path forward. It’s not a marketing gimmick or a passing trend – it’s a smart approach to security that every company should consider. By treating every access attempt with healthy suspicion and rigorously verifying trust at every turn, you can dramatically strengthen your defenses against even the most determined adversaries. Zero Trust may require a mindset change and investment, but it truly lives up to the hype as a cybersecurity game-changer.
