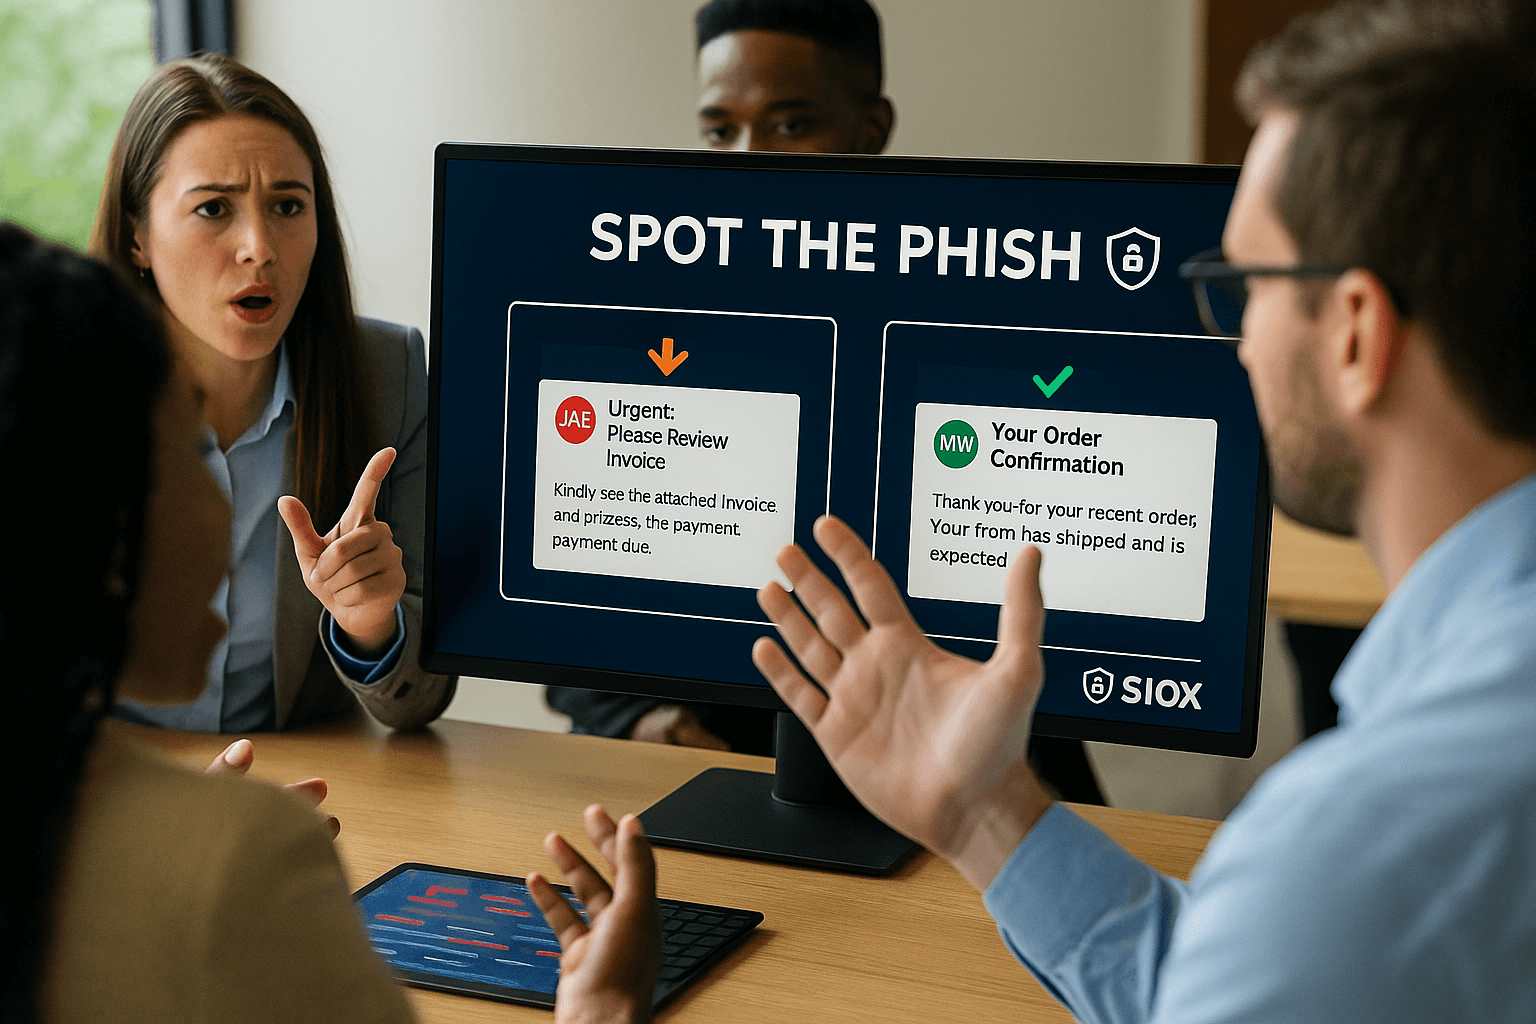
Security Awareness Training educates and tests your workforce on cybersecurity best practices. Since 74% of data breaches involve the human element (errors, phishing clicks, etc.), people truly are the last line of defense. Our program empowers your employees to recognize and avoid threats like phishing emails, suspicious links, social engineering calls, and unsafe behaviors – significantly reducing the risk that a simple mistake could lead to an incident. Delivered as part of SIOX Cyber Defense’s managed platform, this service helps turn your employees into an active defense layer.
We provide interactive, easy-to-follow online courses on topics such as phishing identification, password security, safe internet habits, and physical security. These modules include videos, quizzes, and real-world examples to keep users engaged. Content is updated regularly with the latest threat scenarios (for example, if there’s a surge in CEO fraud scams or USB drop attacks, we incorporate those).
One of the best ways to improve resilience is to simulate phishing attacks and coach employees in the moment. We periodically send out realistic fake phishing emails to your staff (with your permission). If someone clicks, they aren’t punished – instead, they’re redirected to a quick “learning moment” page that explains the red flags they missed. Over time, these simulations significantly decrease click rates as employees get wiser. We provide you with metrics – like who clicked, overall organizational susceptibility trends, etc. – to track improvement.
We introduce friendly competition and rewards to boost engagement. For instance, departments that report the most phish or go longest without a click could be recognized. Our platform often awards badges or points for completing trainings and successfully identifying test phishing emails. This turns security awareness into a positive, team-building experience rather than a boring mandatory chore.
The training platform tracks who has completed each module and who hasn’t, which is useful for compliance requirements (many standards require all employees receive annual security training). We can automate reminder emails to stragglers and even include short quizzes throughout the year to ensure knowledge retention.
We tailor content to your industry and company policies. For example, if you’re a healthcare provider, we include scenarios about protecting patient information and HIPAA guidelines. We can also create special training for executives, who often are targeted by “whaling” (CEO fraud) attacks and may need guidance on how to verify unusual requests that appear to come from them.
Technology alone can’t stop every threat – attackers will inevitably try to trick or misuse your people. A well-trained workforce acts as an extension of your security team: they become adept at spotting that sketchy email or phone call. This can prevent incidents outright (imagine an employee recognizing a phishing email and reporting it, heading off a malware infection). It also fosters a security-conscious culture, so that if something seems off, employees will speak up rather than ignore it. The cost of training is far lower than the cost of even a single breach. Additionally, if a breach does occur, having proof of regular training can reduce your liability and satisfy regulators that you take security seriously. We often say “Employees are the first line of defense.” With our training, that line of defense becomes significantly stronger and more reliable.
+1 (240) 659-0833
We design the training to be concise and impactful. Typically, each module is about 10–15 minutes and can be completed online at the employee’s convenience. We recommend doing one module per month or quarter (rather than a long multi-hour session) so it’s a small time investment spread out. Phishing simulations run in the background during work, so no extra time is needed unless someone falls for one (in which case they spend 2 minutes on a quick remedial lesson). By keeping content snappy and relevant to their daily life (even at home), employees generally find it useful rather than a burden.
Yes, we can customize training by role or department. Developers might get secure coding modules, while finance staff get training on fraud and business email compromise (BEC) scam identification. We also offer more advanced modules for IT/technical groups (like deep dives into social engineering tactics or compliance-focused content). The platform lets you assign modules by group, so each team gets the most relevant content.
We use two main measures: completion and behavioral change. Completion is straightforward – our dashboard shows the percentage of staff that finished each training and their quiz scores (we aim for 100% completion). More importantly, we look at phishing simulation results over time: for example, the click rate on test phishing emails might start around 20% but after a few rounds of training, drop to under 5%. Reporting rates (employees reporting suspicious emails) also tend to increase. These are tangible metrics you can show management to demonstrate improved security posture. Many clients see dramatic improvements within a year – fewer risky clicks and more people proactively reporting threats, clear signs the training is paying off.